Application security from code to architecture
Proofline Security helps organisations identify weaknesses in source code, application architecture and security-critical design decisions.
Specialist expertise in secure code review and security architecture, supported by application testing, threat modelling and broader security assessments.
For organisations that develop or operate business-critical software and need an independent technical security assessment.
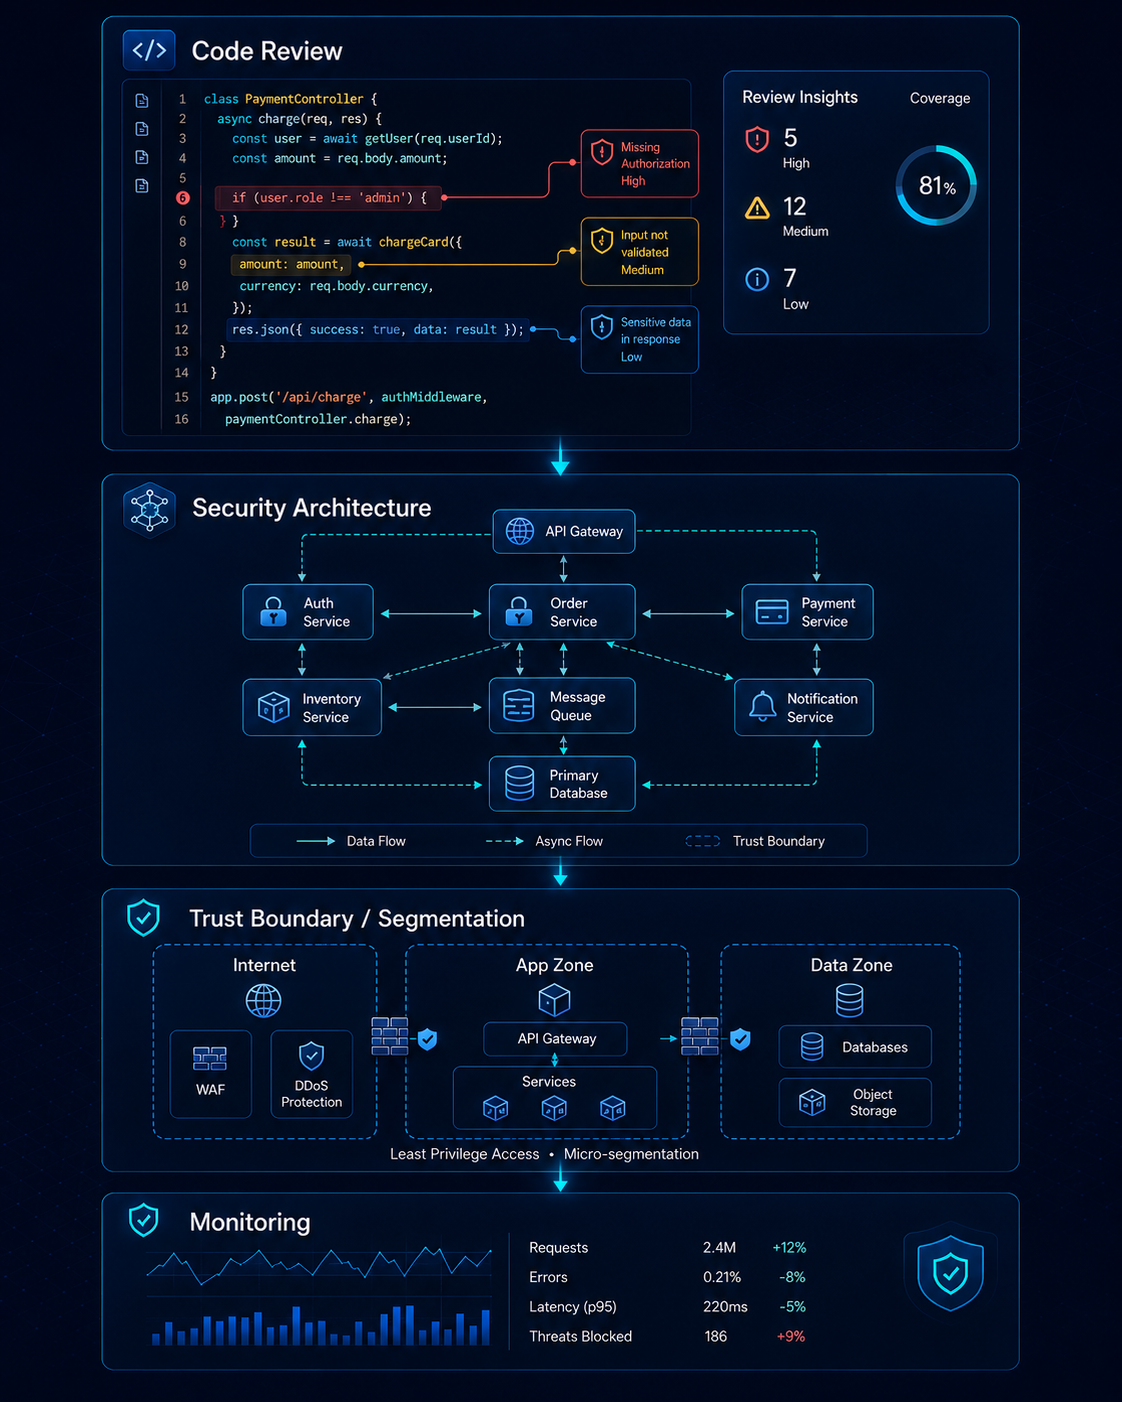
Secure Code Review
We examine source code, application logic and security-critical implementation choices to identify vulnerabilities that automated tools and standard testing may miss.
The focus is on understanding the root cause of weaknesses and providing practical remediation guidance that development teams can act on.
Architecture Security Review
We assess how applications, infrastructure and security controls work together, with particular attention to trust boundaries, identity, network segmentation, monitoring and resilience.
The goal is to identify structural weaknesses that could increase the impact of a compromise or make attacks harder to detect and contain.
Security does not stop at the code
Vulnerabilities rarely exist in isolation. Secure code can still be undermined by weak architecture, excessive network trust, exposed services or insufficient monitoring and detection.
Proofline therefore assesses security in context, from externally visible exposure and application behaviour to architecture, realistic attack scenarios and organisational controls.
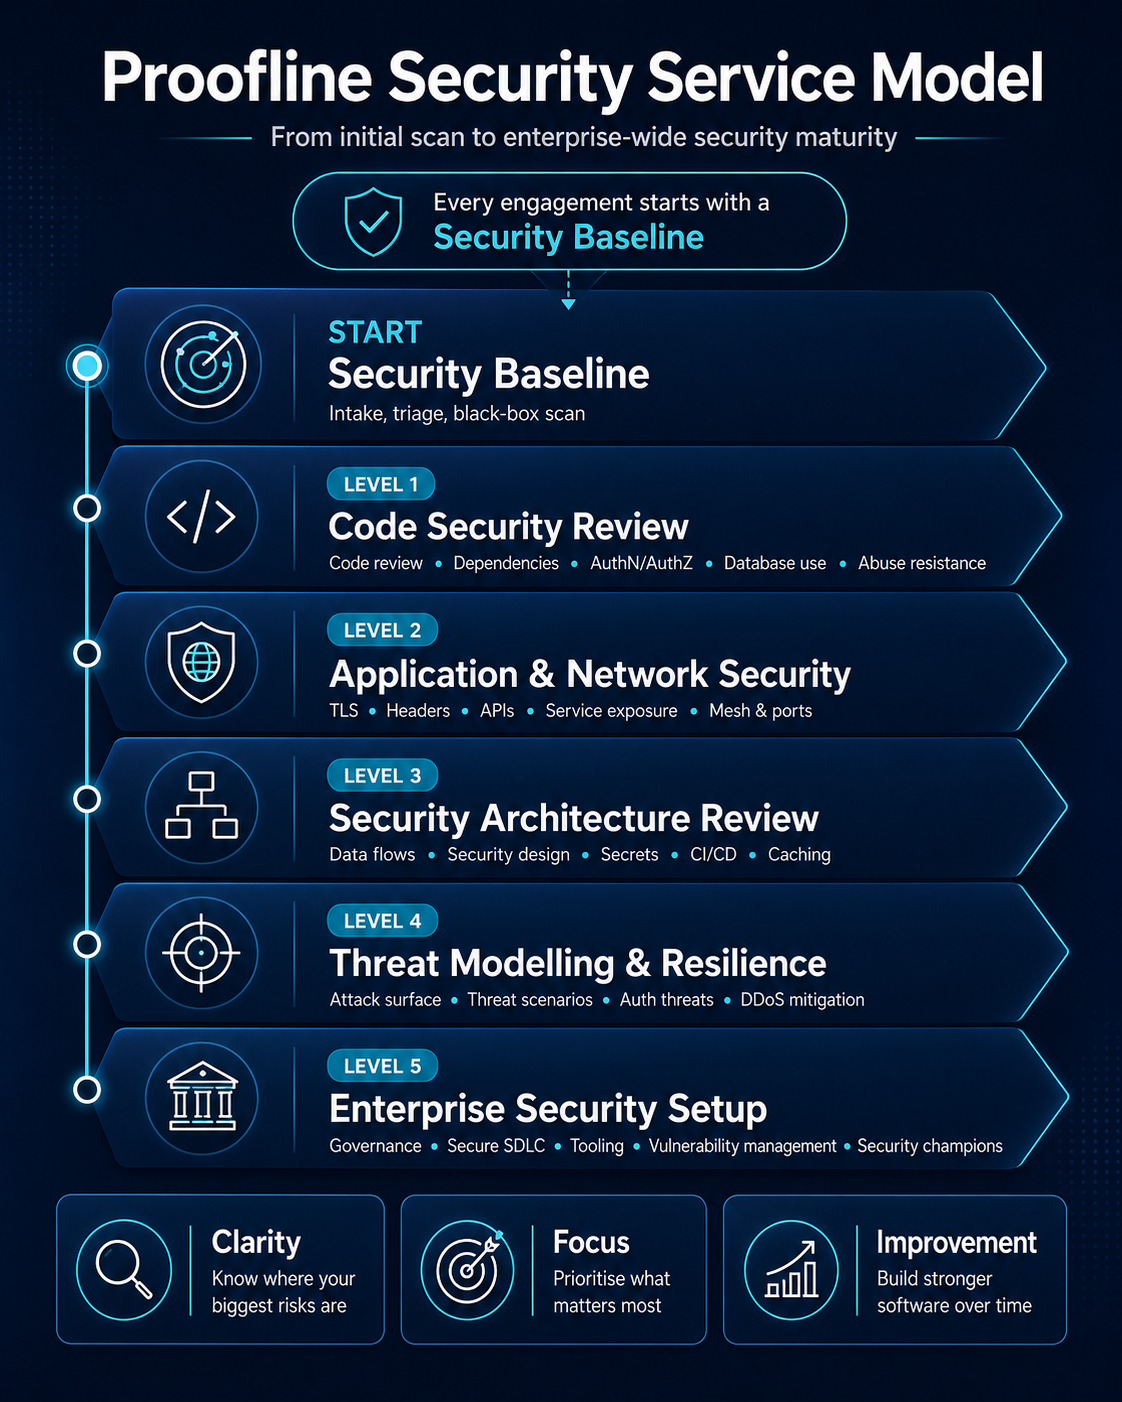
A layered approach to application security.
Proofline Security looks at security as a connected system rather than a collection of isolated checks.
Every engagement starts with a baseline to understand exposure, context and risk. From there, assessments can move deeper into source code, running applications, network and security architecture, realistic threat scenarios and, where relevant, organisation-wide security practices.
Our strongest specialisations are secure code review and security architecture, but both are most effective when considered in the wider context of how systems are exposed, connected, monitored and operated.
The result is a focused assessment that helps identify not only what is vulnerable, but also why the weakness exists, how far an attacker could get and which improvements matter most.
Built on real-world software engineering experience.
Effective security reviews require more than knowledge of vulnerabilities and tooling. They require an understanding of how software is actually designed, built, scaled and operated.
Proofline Security combines deep software engineering and architecture experience with specialised cybersecurity expertise. This helps us assess not only whether security controls exist, but whether they are implemented correctly, placed at the right level and effective within the wider system.
Independent • Confidential • Evidence-based • Developer-focused