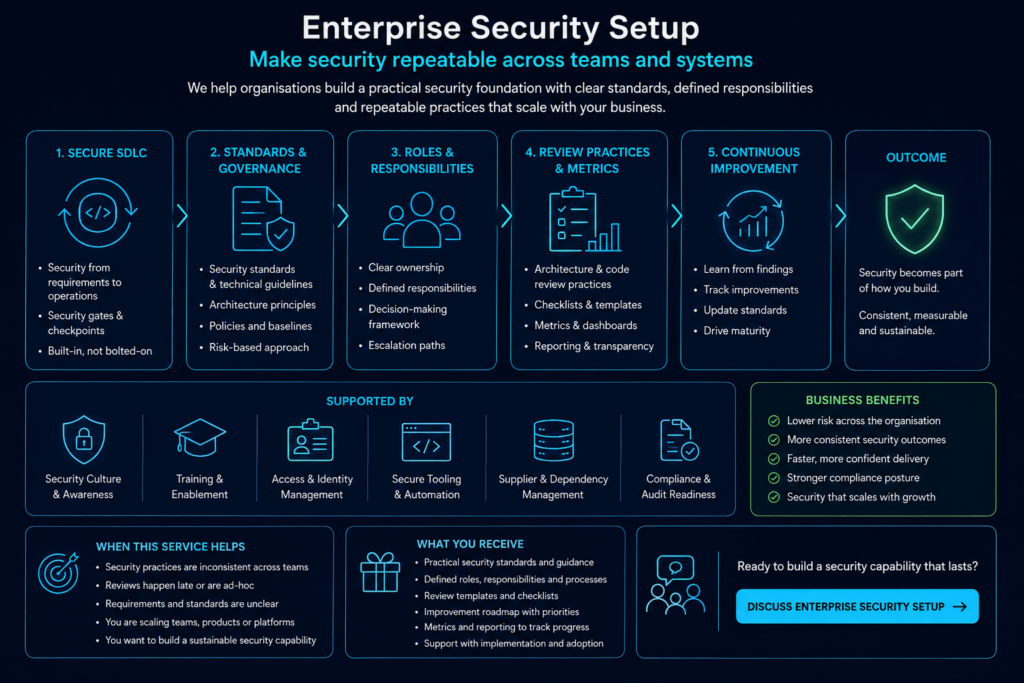
Make security repeatable across teams and systems
We help organisations turn one-off security efforts into a structured and sustainable capabilities.
The focus is on practical standards, clear responsibilities and repeatable security practices that fit the organisation, its development process and its technical landscape.
What we help establish
- secure development lifecycle practices
- security standards and technical guidelines
- roles, ownership and decision-making
- architecture and code review practices
- risk-based security requirements
- security metrics and reporting
- supplier and dependency expectations
- continuous improvement processes
What this helps solve
- security depends too heavily on individual experts
- teams apply different standards
- reviews happen late or inconsistently
- security requirements are unclear
- architecture decisions lack a repeatable review process
- findings are not translated into lasting improvements
- growth has made informal practices difficult to maintain
Practical, not ceremonial
The setup is tailored to the organisation’s size, maturity and risk profile.
This may include lightweight standards, review templates, decision records, secure development checkpoints, escalation paths and measurable improvement goals.
The result should support delivery rather than slow it down.
Security in context
Enterprise Security Setup builds on the lessons from code reviews, architecture assessments and threat modelling.
It helps turn individual findings into organisation-wide improvements that can be applied consistently across future systems and projects.